
Posts tagged “Express”
Express logging in production: pino-http vs morgan, request bodies and redaction
morgan, pino-http or winston? A production Express logging setup on Express 5: one JSON line per request with request ID, route and user, bodies for failed requests only, pino redaction, and errors on the same line.
Node.js API logging: what to log for every request, and how
Most Node.js API logs can't answer "what happened to this customer's request?" This guide covers the six fields every request line needs, safe body capture that keeps streaming intact, redaction, outbound calls, and the queries to run, with code tested on Node 22 and 24.

Express monitoring: route-level metrics, APM and alerts for Express 4 and 5
Most Express metrics are labelled by raw URL and miss async errors. Build route-level metrics with prom-client, add OpenTelemetry in the right load order, and set alerts, with code we ran on Express 4.22.3 and 5.3.0.
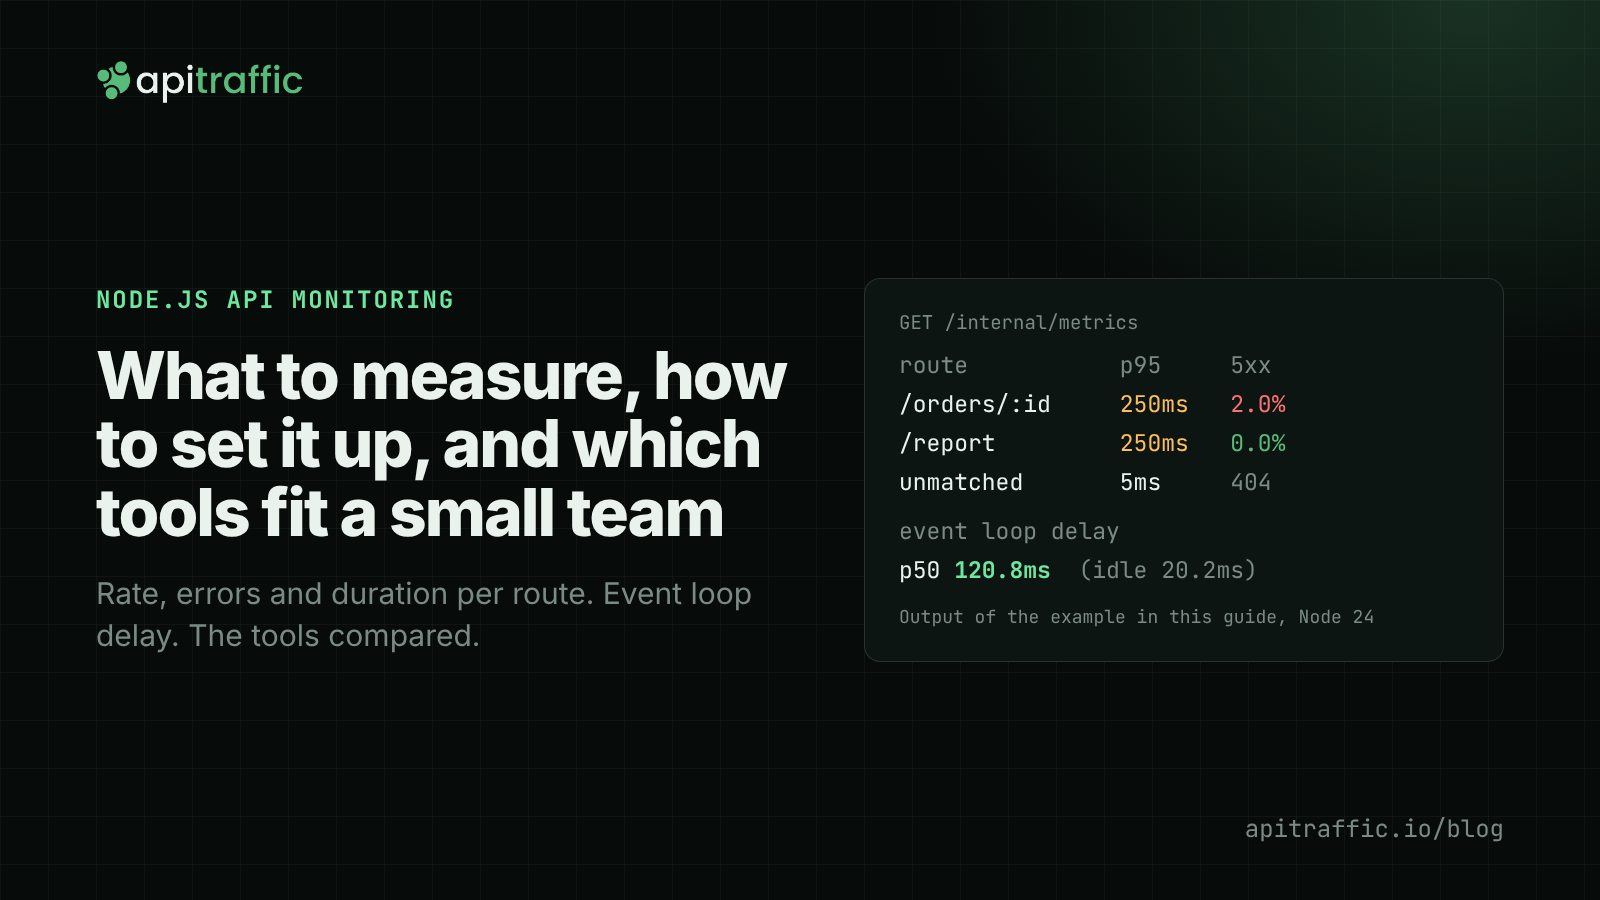
Node.js API monitoring: what to measure, how to set it up, and which tools fit a small team
Uptime checks miss most of what breaks a Node API. What to measure per route and per process, a tested Express middleware for RED metrics and event loop delay, where OpenTelemetry fits, a fair tool comparison and the alerts worth paging on.
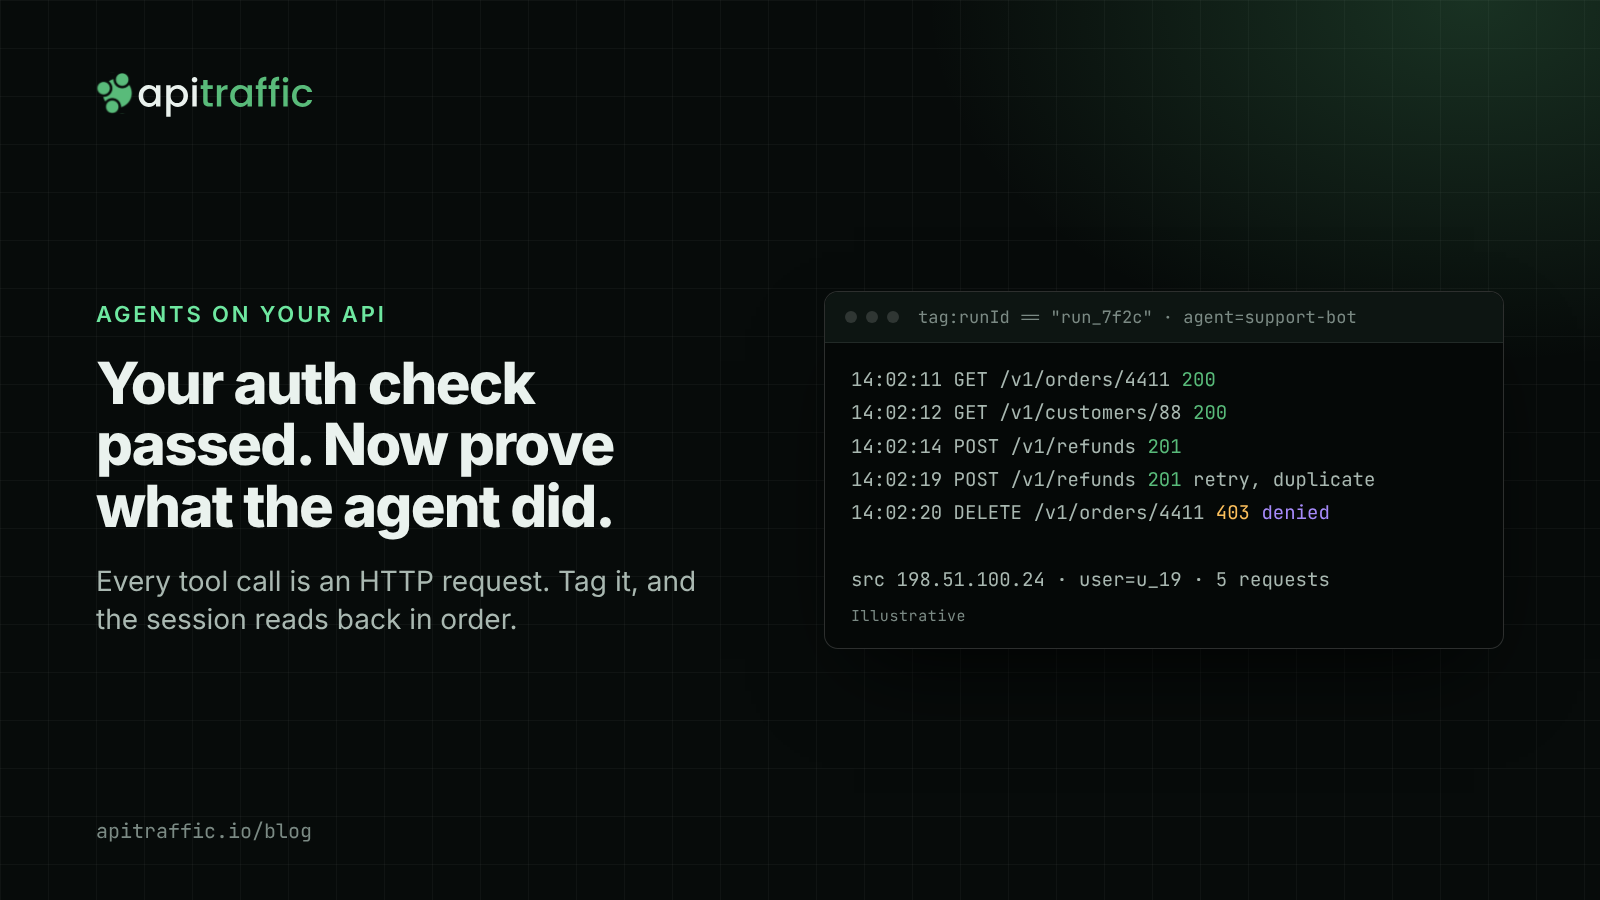
Your auth check passed. Now prove what the agent did.
An agent calls your API with a valid token, the scopes allow it, and the write lands with a clean 201. Nobody asked for it. Here's how to fix authorization for agents first, then build an audit trail that shows exactly what the agent did.
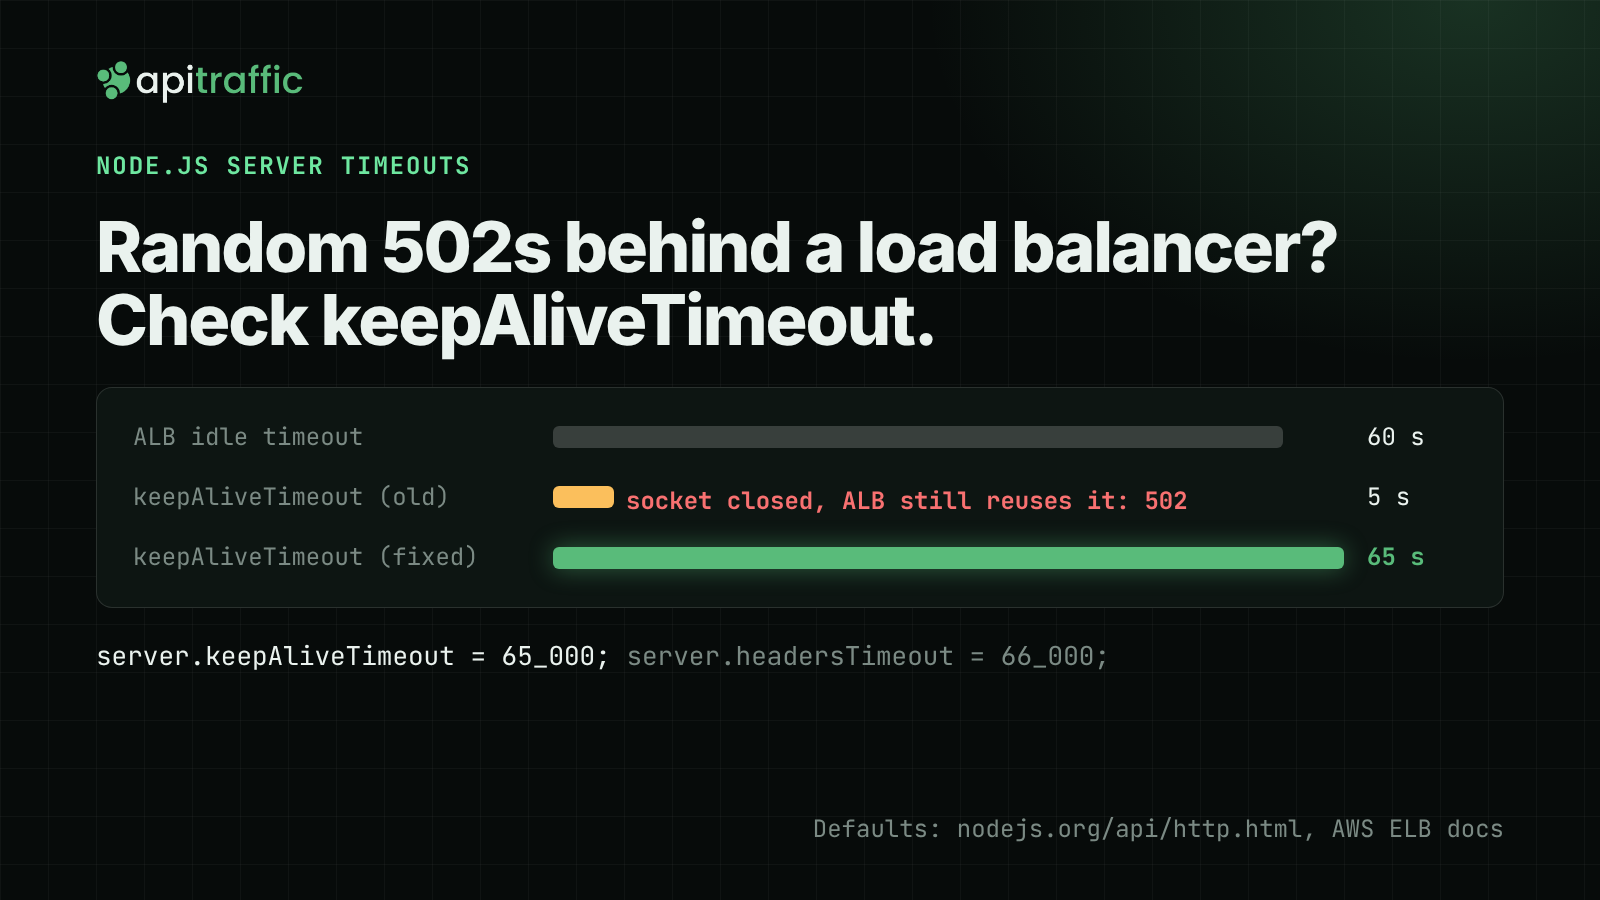
Node.js server timeouts: requestTimeout, headersTimeout and keepAliveTimeout
Random 502s behind a load balancer often come down to one setting: keepAliveTimeout. What each Node.js server timeout controls, safe values behind an AWS ALB, and how to confirm the fix.
Observability for a 5-person Node team: what each option actually gives you
When a customer says the export failed again, how long until you see the exact request? For most small Node teams the answer is spread across three tools. Here's what each option is built for, the gaps that bite, and a setup you can copy.

API business logic abuse: requests that are valid but wrong
Akamai says 61% of API attacks in 2025 involved unauthorized workflows, double the year before. Four examples for a small SaaS, how to map the expected order of calls, and Express code to catch the ones that skip a step.
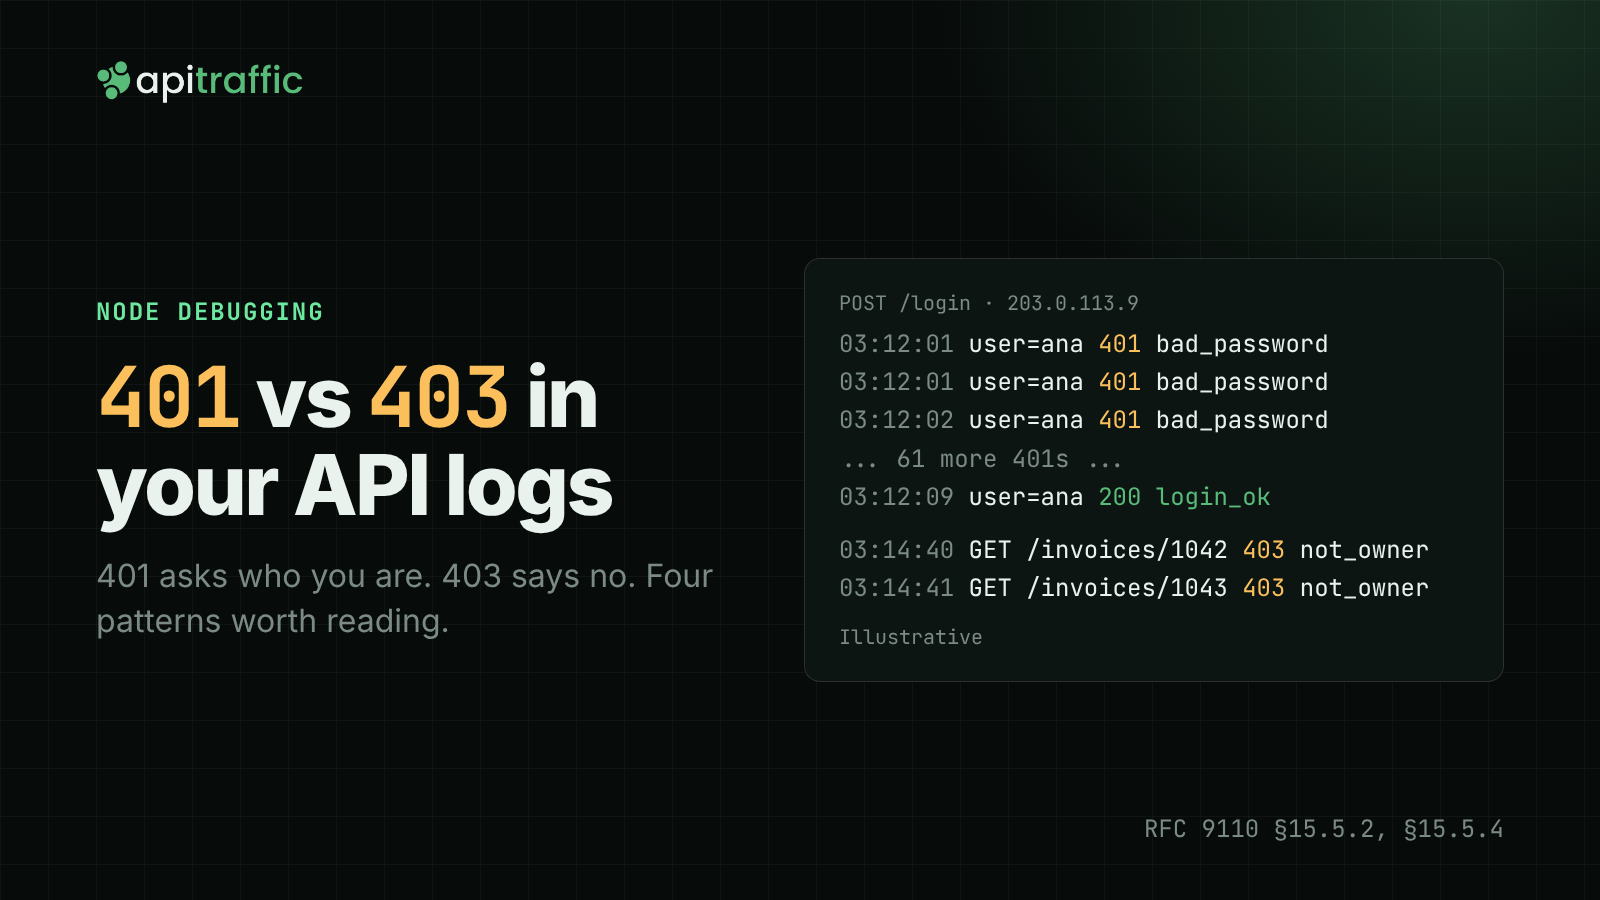
401 vs 403 in your Node API logs: what each pattern means
401 and 403 look alike in a log but answer different questions. What each means under RFC 9110, four auth patterns worth an alert, how to return the right one in Express and Fastify, and five searches to run on last week's logs.
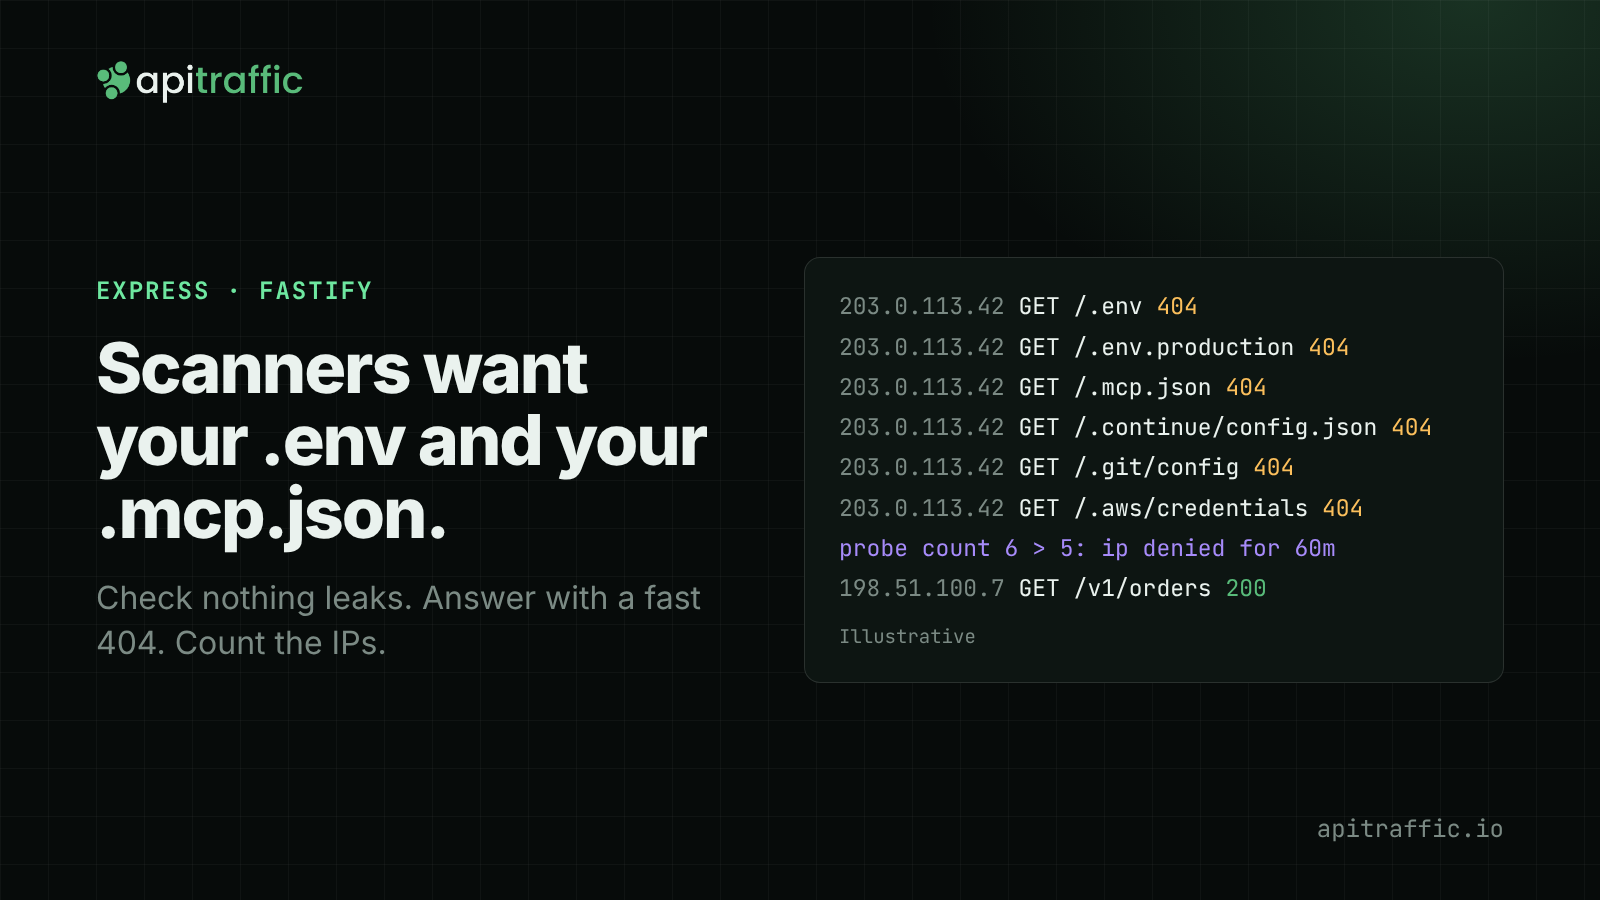
Block .env and config-file probes in Express and Fastify
One site logged 1,028 requests for credential paths in a day, including /.mcp.json and other AI tool configs. How to check none can succeed, return a fast 404 in Express and Fastify, and block the IPs doing it.
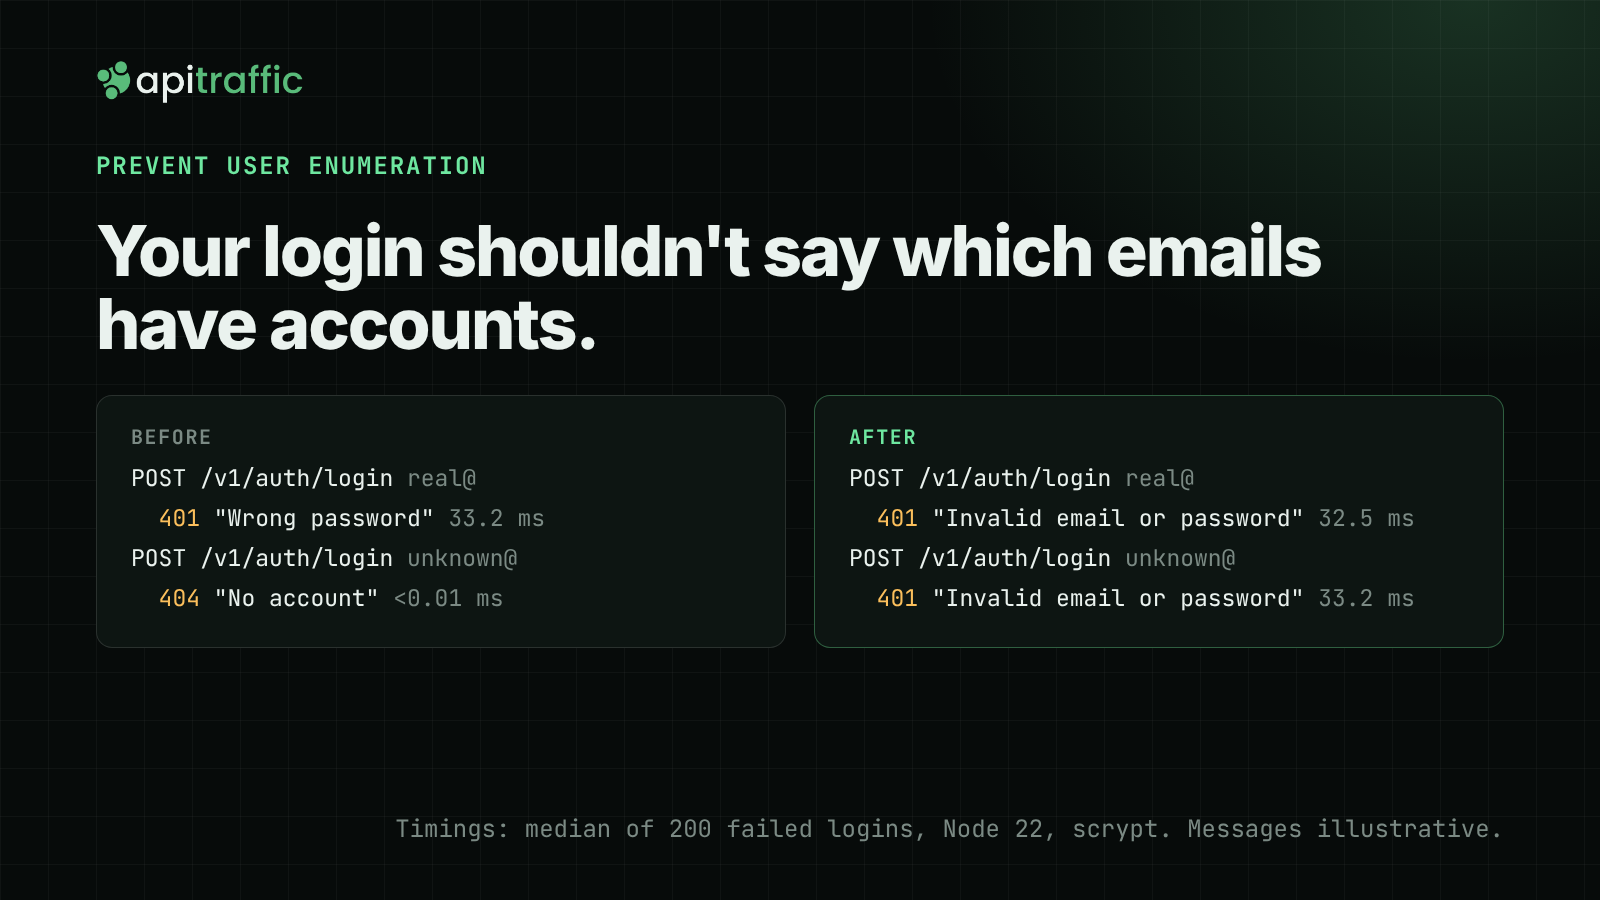
Stop user enumeration on your Node.js login, signup and reset endpoints
AI agents made hundreds of millions of requests to login pages in the first half of 2026. If your API answers differently for real and unknown emails, it hands them a target list. Here's how to make login, reset and signup give one answer.
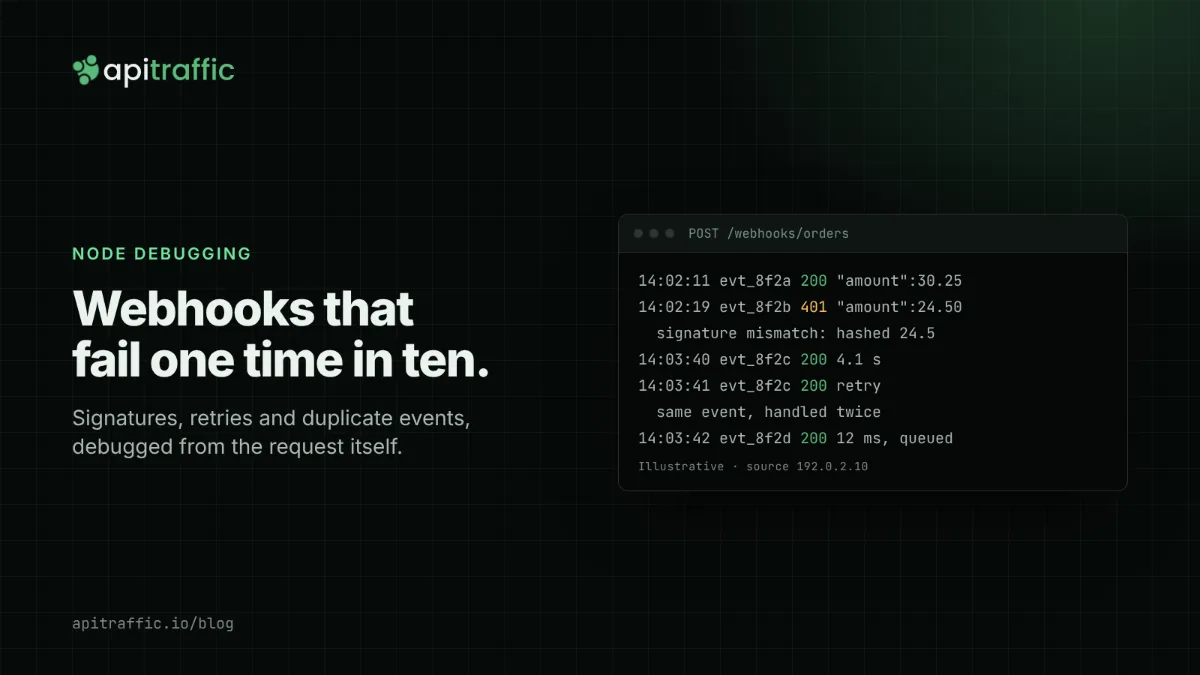
Debugging webhooks in Node: failed signatures, retries and duplicate events
Webhook bugs rarely reproduce on your laptop: a signature check that fails one time in ten, the same event processed twice, a retry storm after a slow deploy. Here's the fix for each, plus how to get the exact request in front of you.